Key takeaway
- Build a Jenkins continuous delivery pipeline: Docker setup, Jenkinsfile, GitLab webhooks, Kubernetes agents and secure credentials, per official docs.
A Jenkins continuous delivery pipeline turns every commit into a build that is tested, packaged and ready to release. You describe the pipeline in a Jenkinsfile kept in source control, run Jenkins from the official jenkins/jenkins image, connect it to GitLab with webhooks, and run builds on Kubernetes agents if you want them isolated and disposable.
This guide covers the current approach: Pipeline as code, a maintained Docker image, scoped credentials and a clear view of what Jenkins does and does not do. For the wider picture, read what continuous delivery is, with tools and best practices.
What is continuous delivery, and where does Jenkins fit?
DORA defines continuous delivery as "the ability to release changes of all kinds on demand quickly, safely, and sustainably" (dora.dev, read 13 November 2026). It lists test automation, deployment automation, continuous integration, version control, trunk-based development and monitoring among the supporting practices. DORA also separates it from continuous deployment, which pushes every change to production as soon as possible.
Jenkins is the automation server that runs these steps. It describes Pipeline as a suite of plugins that supports implementing and integrating continuous delivery pipelines (jenkins.io). Jenkins does not decide what is safe to release. That comes from your tests, your review rules and your release policy.
How do you run Jenkins in Docker today?
Older tutorials use jenkins:alpine. Docker Hub marks the official jenkins image as deprecated, says it has not been updated for over two years, and points to jenkins/jenkins:lts (Docker Hub). The Jenkins Docker guide uses tags such as jenkins/jenkins:lts-jdk21 and lists Java 21 or later as a requirement (jenkins.io, read 13 November 2026).
| Item | What the Jenkins guide says | Why it matters |
|---|---|---|
| Image | Official jenkins/jenkins; lts tags track the stable LTS line, latest tracks the weekly release | Pin an LTS tag for a pipeline that other teams depend on |
| Port 8080 | The web interface | Put it behind HTTPS before exposing it |
| Port 50000 | Inbound agent traffic over TCP; WebSocket agents do not need it | Open it only if you use inbound agents |
| Volume | jenkins-data mapped to /var/jenkins_home | Keeps jobs, plugins and configuration across container restarts |
| First login | Read /var/jenkins_home/secrets/initialAdminPassword or the container log, then complete the setup wizard | Do not skip the wizard: the security guide warns that skipping it may leave the instance insecurely configured |
The official image does not include the Docker CLI. If your jobs build images, the guide adds it in a custom image and runs a Docker-in-Docker sidecar. Check the page for the current commands rather than copying older ones.
How do you define the pipeline as code?
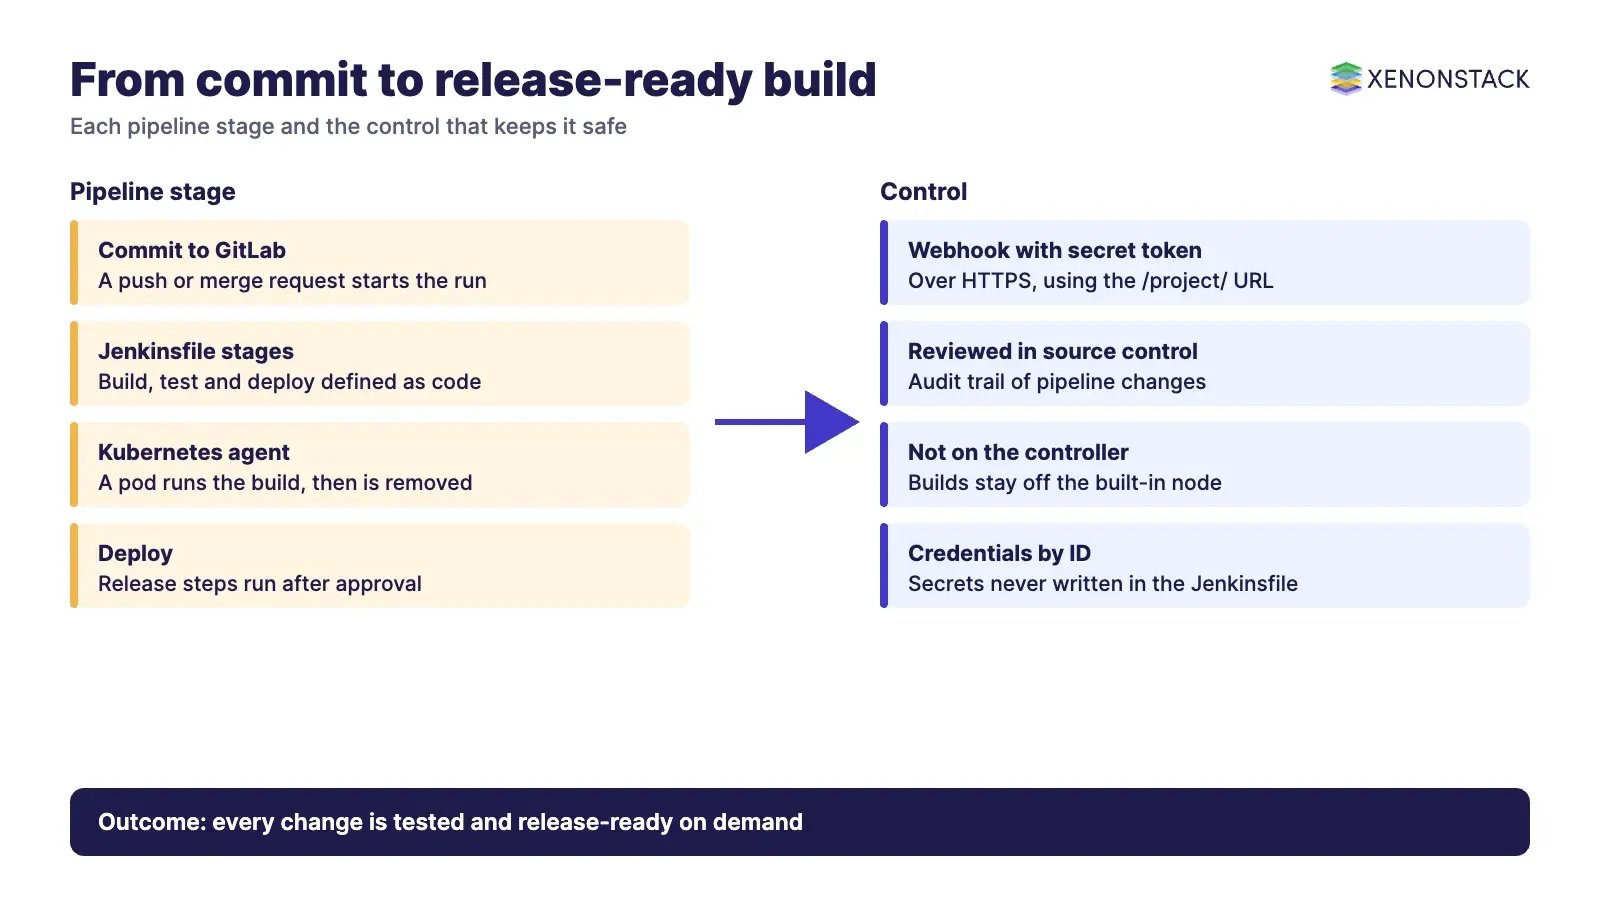
A Jenkinsfile is a text file that holds the pipeline definition and can be committed to the project repository. Jenkins lists the benefits: a build process for every branch and pull request, review alongside the code, an audit trail of pipeline changes and a single source of truth for the team. It calls this generally considered best practice (jenkins.io). Freestyle jobs configured in the interface keep that logic outside version control.
Declarative Pipeline is designed to make pipeline code easier to write and read. The agent directive, stages and steps are required. A minimal shape, taken from the Jenkins documentation, looks like this:
pipeline {
    agent any
    stages {
        stage('Build') {
            steps { echo 'Building..' }
        }
        stage('Test') {
            steps { sh 'make check' }
        }
        stage('Deploy') {
            steps { sh 'make publish' }
        }
    }
}
Replace the example commands with your own build, test and deploy steps. Keep the deploy stage behind whatever approval your release policy needs. See the Jenkinsfile documentation for syntax.
How do you connect GitLab to Jenkins?
Install the GitLab plugin. Its page says it lets GitLab trigger Jenkins builds on pushes and merge requests, and can send build status back to GitLab (plugins.jenkins.io, read 13 November 2026). It is community-developed and not formally supported by GitLab Inc. or CloudBees Inc., and its page lists past security advisories, so keep it updated.
| Step | What the plugin page says |
|---|---|
| Webhook URL | https://JENKINS_URL/project/PROJECT_NAME, or .../project/FOLDER/PROJECT_NAME for jobs in a folder. Do not use the standard /job/.../build URLs, which bypass the plugin |
| Webhook authentication | Generate a per-job secret token under the job's GitLab settings (Advanced) and paste it into the webhook's Secret Token field. Use HTTPS for all connections |
| Build status back to GitLab | Add a Jenkins credential of the kind GitLab API token, created from a GitLab access token with the api scope |
| Cloning the repository | Configured separately in the Git plugin. The GitLab API token is not used for cloning |
How do you run builds on Kubernetes?
The Jenkins Kubernetes plugin runs dynamic agents in a cluster: it creates a pod for each agent it starts and removes it after each build, and the controller does not need to run inside Kubernetes (plugins.jenkins.io, read 13 November 2026). It needs a running cluster and a ServiceAccount with enough privileges. Check the plugin page for the current Jenkins and Kubernetes version requirements. The plugin page gives this minimal example:
podTemplate {
    node(POD_LABEL) {
        stage('Run shell') {
            sh 'echo hello world'
        }
    }
}
For a full controller setup on a cluster, follow Jenkins on Kubernetes with Helm and YAML. For the same idea on a managed cloud service, see building a DevOps pipeline on AWS.
How do you keep the pipeline secure?
- Use Jenkins credentials. Jenkins stores them encrypted on the controller and pipelines use them by ID, which limits exposure to users (jenkins.io). Reference them with the
credentials()helper, not as text in the Jenkinsfile. - Keep secrets out of Groovy strings. The Jenkinsfile guide warns that Groovy interpolation expands a token before the command reaches the agent. Send a literal command to
shso the shell reads the secret from its environment. - Do not build on the controller. The security guide says builds should not run on the built-in node, and that this is only the start of controller isolation (jenkins.io).
- Review multibranch and organisation folder access. The same guide notes that credentials there may be reachable by unprivileged users in ways you did not anticipate.
For where security checks sit in the pipeline, read DevSecOps in CI/CD and infrastructure as code security.
When is Jenkins the right choice, and when is it not?
| Situation | Fit | Reason |
|---|---|---|
| You need a self-hosted server with plugin integrations and full control of agents | Good fit | Jenkins runs on your infrastructure and its Pipeline plugins are maintained by the Jenkins project |
| You want pipeline logic reviewed with the code | Good fit | A Jenkinsfile in source control gives review and an audit trail |
| Your team wants no server to patch | Weaker fit | You own upgrades, plugin updates and controller security. Compare hosted CI in your source platform |
| You rely on many community plugins | Check each one | Plugins have their own maintainers and advisories. Review the plugin page before adopting |
Whatever the tool, measure the result. DevOps metrics: the DORA five and what to add shows how to track delivery speed and stability.
What sequence should a team follow?
- Run Jenkins from a pinned
jenkins/jenkinsLTS tag with a persistent volume and complete the setup wizard. - Move build, test and deploy steps into a Jenkinsfile in the repository.
- Connect GitLab with a webhook and a secret token over HTTPS.
- Move secrets to Jenkins credentials and stop builds running on the controller.
- Run agents as Kubernetes pods if you need clean, disposable build environments.
- Track change lead time and failure rate, and tighten the pipeline from there.
As agents begin to propose and trigger release changes, the pipeline needs a record of which policy allowed each one. ElixirData Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, and ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control.
To map one release decision your agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is a continuous delivery pipeline in Jenkins?
It is an automated path from a code commit to a release-ready build, defined in a Jenkinsfile. Jenkins describes Pipeline as a suite of plugins that supports implementing and integrating continuous delivery pipelines into Jenkins.
Should I still use the jenkins:alpine Docker image?
No. Docker Hub states that the official jenkins image is deprecated and points to jenkins/jenkins:lts, which the Jenkins community maintains. Jenkins's Docker guide uses tags such as lts-jdk21.
How does GitLab trigger a Jenkins build?
Through the GitLab plugin and a webhook that points to https://JENKINS_URL/project/PROJECT_NAME. The plugin page advises against the standard /job/.../build URLs, because they bypass the plugin, and recommends HTTPS.
Where should pipeline secrets live?
In Jenkins credentials, referenced by ID with the credentials() helper, never written into the Jenkinsfile. Jenkins stores credentials in encrypted form on the controller and pipelines use them only by ID.
Is continuous delivery the same as continuous deployment?
No. DORA defines continuous delivery as the ability to release changes of all kinds on demand quickly, safely and sustainably. Continuous deployment pushes every change to production as soon as possible, which does not suit every type of software.
Follow XenonStack on LinkedIn: XenonStack on LinkedIn for new guides on agentic AI, data and platform engineering.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE