Key takeaway
- CVE-2020-5135 (SonicOS buffer overflow) and CVE-2019-1405 (Windows UPnP privilege escalation): what they are, affected versions, scores and how to respond.
CVE-2020-5135 is a critical buffer overflow in SonicWall SonicOS that a remote attacker can use to crash a firewall or possibly run code, and CVE-2019-1405 is a local privilege escalation flaw in the Windows UPnP service. Both were added to the CISA Known Exploited Vulnerabilities catalogue on 15 March 2022, which means exploitation has been observed.
This guide is for security and IT operations teams that run SonicWall firewalls or Windows systems and want to know what each flaw is, how they differ, and how to respond. It also links the Cyber Security Services page for wider security work. Facts come from the NVD, CIRCL and vendor pages linked in the text.
What is CVE-2020-5135 in SonicWall SonicOS?
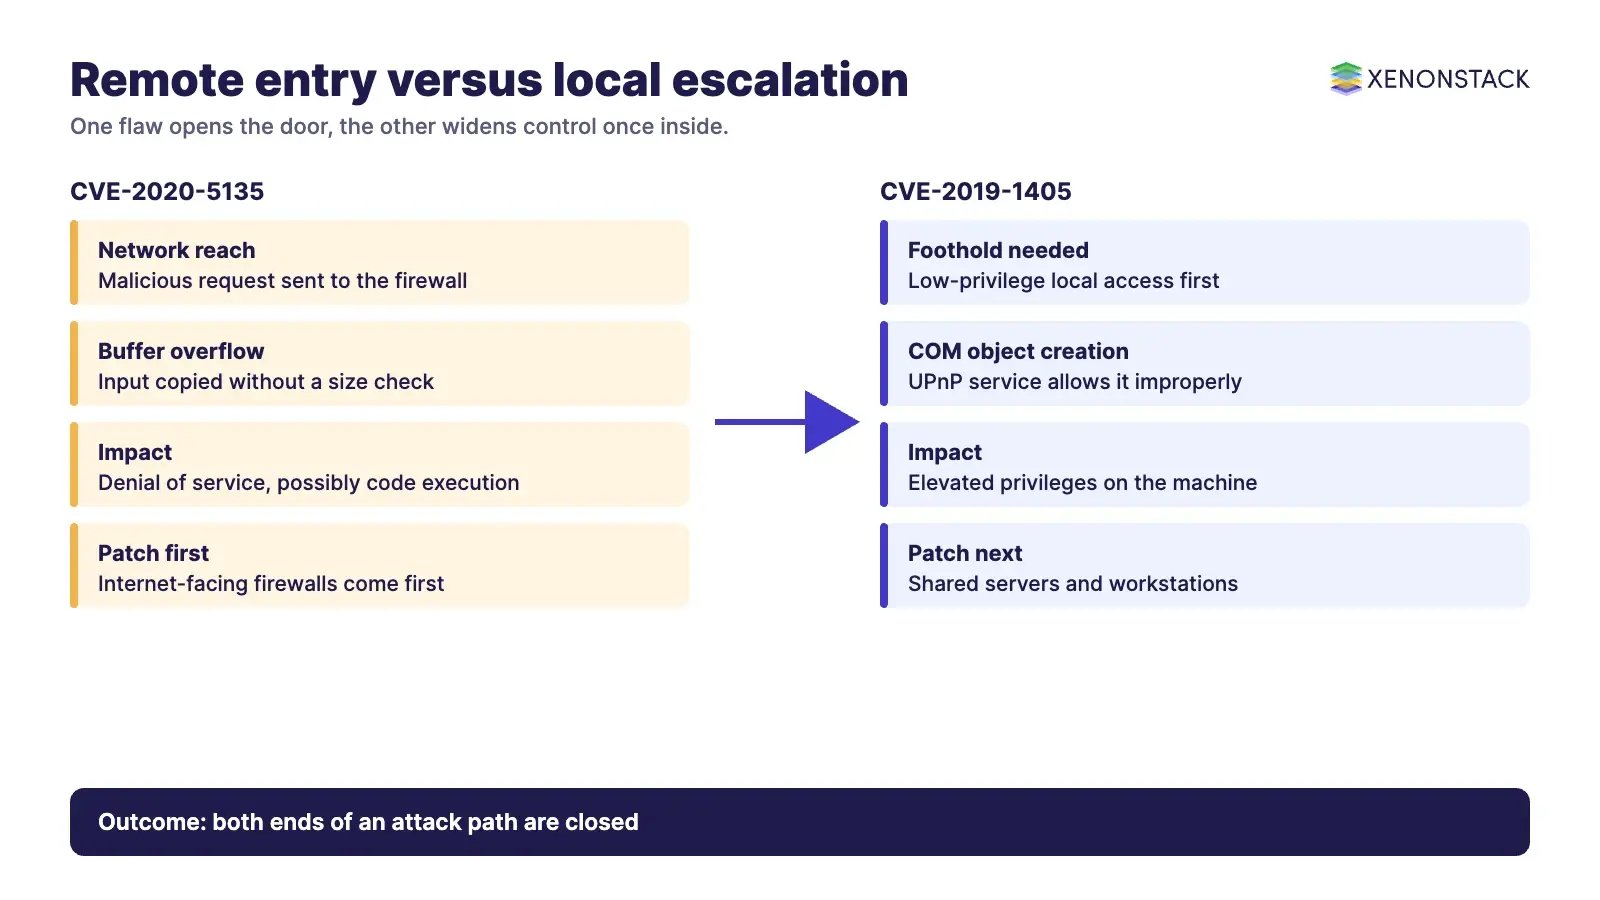
The NVD record for CVE-2020-5135 describes a buffer overflow in SonicOS that lets a remote attacker cause a denial of service and possibly execute arbitrary code by sending a malicious request to the firewall. It names SonicOS Gen 6 versions 6.5.4.7, 6.5.1.12 and 6.0.5.3, SonicOSv 6.5.4.v and Gen 7 7.0.0.0 as affected. The weakness type is CWE-120, a classic buffer copy without checking input size.
NVD shows it was published on 12 October 2020, scored 9.8 Critical on CVSS v3.1 (7.5 High on the older v2.0 scale), and entered the CISA catalogue on 15 March 2022 with the required action "Apply updates per vendor instructions" and a due date of 5 April 2022. The vendor reference is the SonicWall advisory SNWLID-2020-0010, which is the place to confirm fixed builds. Use that advisory rather than a copied version list, because firmware lines change.
What is CVE-2019-1405 in the Windows UPnP service?
The CIRCL vulnerability record for CVE-2019-1405 reproduces the Microsoft description: the Windows Universal Plug and Play (UPnP) service improperly allows COM object creation, which gives an elevation of privilege. The Microsoft vendor reference is the Microsoft Security Update Guide entry. The weakness is recorded by Microsoft as CWE-269, improper privilege management.
The CVSS v3.1 base score is 7.8 High with the vector AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H. In plain words, the attacker must already be able to run code on the machine with a low-privilege account, but needs no user interaction and can then gain high impact. The record was published on 12 November 2019 and, per the same page, CISA added it to its catalogue on 15 March 2022. That page also lists known ransomware campaign use as "Known".
The affected list is wide. It includes Windows 7 SP1, 8.1, RT 8.1 and Windows 10 versions 1607, 1709, 1803, 1809 and 1903, plus Windows Server 2008, 2008 R2, 2012, 2012 R2, 2016, 2019 and server versions 1803 and 1903. Some write-ups name only Windows 10 1803, which understates the exposure. If you still run any listed release, confirm it receives security updates.
How do the two vulnerabilities differ?
| Item | CVE-2020-5135 (SonicOS) | CVE-2019-1405 (Windows UPnP) |
|---|---|---|
| Flaw | Buffer overflow (CWE-120) | Improper COM object creation, privilege escalation (CWE-269) |
| Attacker position | Remote, over the network | Local, with a low-privilege account |
| Likely outcome | Denial of service, possibly code execution | Elevated privileges on the machine |
| CVSS v3.1 | 9.8 Critical (AV:N/AC:L/PR:N/UI:N) | 7.8 High (AV:L/AC:L/PR:L/UI:N) |
| Published | 12 October 2020 | 12 November 2019 |
| CISA catalogue | Added 15 March 2022, due 5 April 2022 | Added 15 March 2022, due 5 April 2022 |
| Fix | Vendor-fixed SonicOS build (see advisory) | Microsoft security update (see advisory) |
Why does a local flaw still matter?
A remote flaw such as CVE-2020-5135 is an entry point on a device that faces the internet. A local flaw such as CVE-2019-1405 is a step after entry: an attacker who already has a foothold on a workstation or server can use it to gain wider control. Teams that rank only by network reachability can therefore under-rate it. Its place in the CISA catalogue, and the ransomware note on the CIRCL page, are reasons to patch it despite the lower score.
How should you respond?
- List every SonicWall appliance and its SonicOS build, and every Windows system in the affected releases.
- Compare each build with the vendor advisories and apply the listed fixes.
- Check whether the SSL VPN or other management services of a firewall face the internet, and reduce that exposure until the patch is in.
- Limit who has local interactive access to servers, so a low-privilege foothold is harder to obtain.
- Review logs for crashes or unusual activity before the patch date.
- Record what was patched, when and who approved it.
How do AI agents change vulnerability response?
Advisories name products and versions, while your estate is described in an inventory, a ticket queue and a change calendar. AI agents can connect the two: read an advisory, find the matching assets, draft the change and flag what needs a human decision. The agent is only as good as the context it is given, so it needs asset ownership, exposure and change policy to be clear. ElixirClaw is XenonStack's AI agents computing platform for building and running agent workflows like this, with people approving production changes.
What should you do first?
- Find all SonicOS appliances and Windows systems in the lists above.
- Patch the internet-facing firewalls first.
- Patch the Windows systems that several people can log in to.
- Add the CISA catalogue to your regular patch review.
- Agree who can approve an emergency change.
To map one security decision your agents make, and the data and policy it depends on, book a Context Workshop. See what happens in the workshop.
For more advisories, explore more critical vulnerabilities and their remediations.
Frequently asked questions
What is CVE-2020-5135?
It is a buffer overflow in SonicWall SonicOS. NVD says a remote attacker can cause a denial of service and possibly execute arbitrary code by sending a malicious request to the firewall.
What is CVE-2019-1405?
It is an elevation of privilege flaw in the Windows UPnP service, which improperly allows COM object creation. It scores 7.8 High on CVSS v3.1.
Can CVE-2019-1405 be exploited remotely?
The CVSS vector is local, so the attacker needs to run code on the machine first. It is used after a foothold is gained, not as a first entry point.
Are these vulnerabilities being exploited?
Both were added to the CISA Known Exploited Vulnerabilities catalogue on 15 March 2022, which indicates observed exploitation.
How do I fix CVE-2020-5135?
Upgrade SonicOS to a fixed build listed in the SonicWall advisory SNWLID-2020-0010.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE