Key takeaway
- Sanity testing is a quick, focused check that a fix or small change works before wider testing. See how it differs from smoke and regression testing.
What is sanity testing?
Sanity testing is a quick, narrow check that a specific bug fix or small change works as intended, run on a build that has already passed its first checks. It tells the team whether the build is worth deeper effort or should go straight back to the developer. It is usually treated as a focused subset of regression testing.
Terminology varies. The ISTQB glossary, as reproduced on istqb-glossary.page lists "sanity test" as a synonym of smoke test, while many teams use the two words for different checks. This guide uses the common team meaning: smoke checks ask whether the build is stable at all, sanity checks ask whether the change just made behaves sensibly. For a side-by-side view, read our smoke testing vs sanity testing guide.
How does sanity testing work?
A sanity test follows a short sequence. It is usually unscripted or lightly scripted, so the value comes from choosing the right few checks.
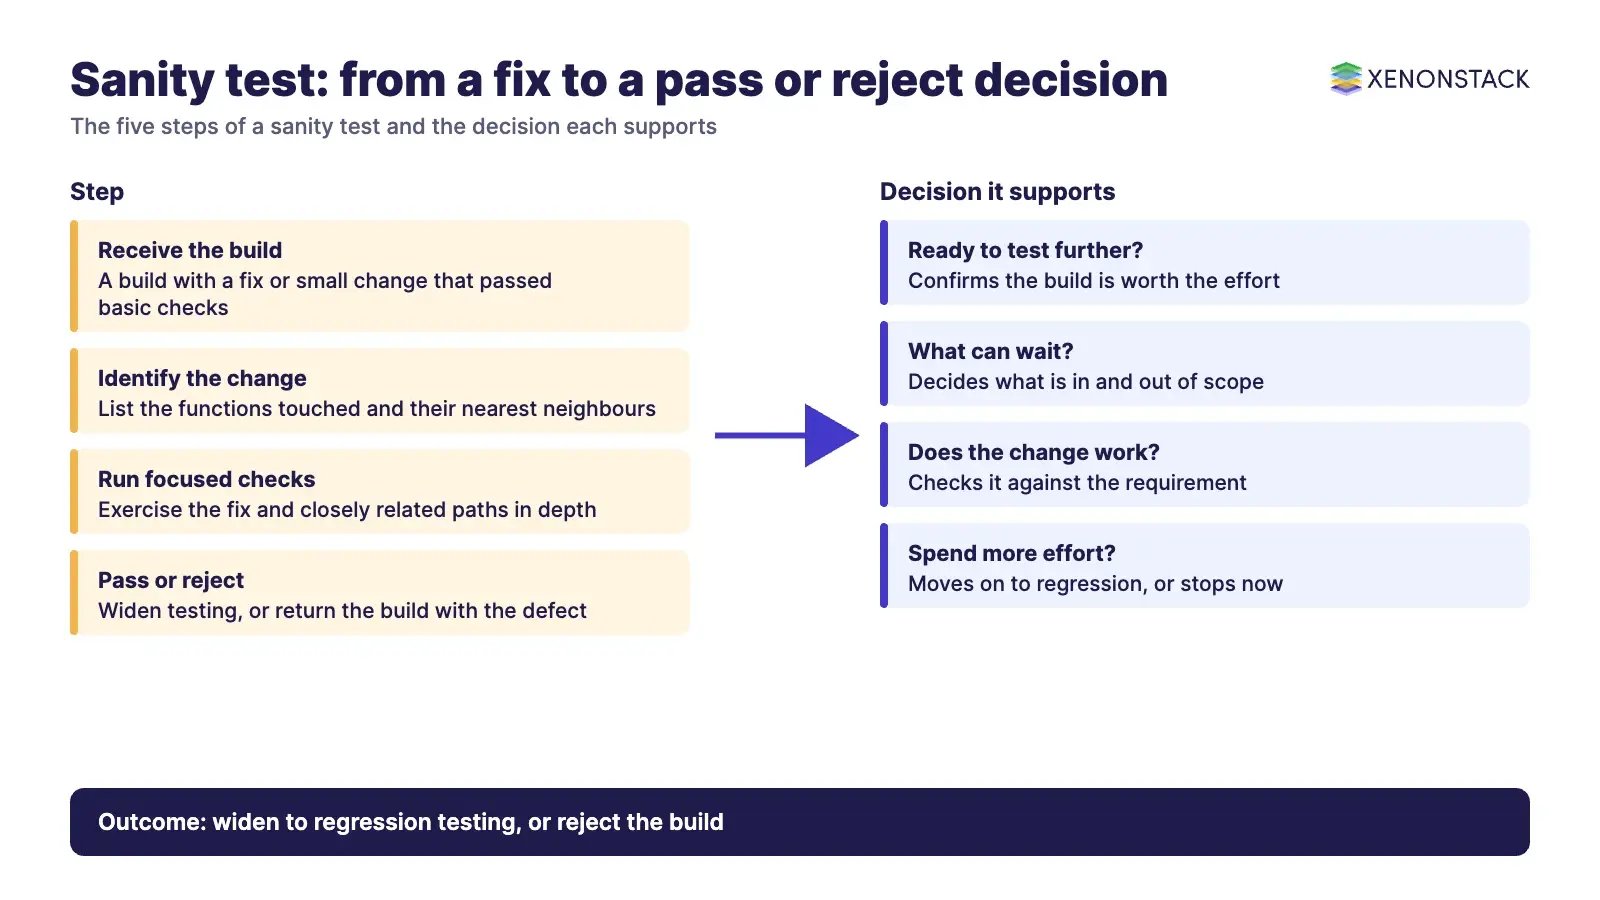
| Step | What happens | Decision it supports |
|---|---|---|
| 1. Receive the build | A build arrives with a fix or a small change, after it has passed basic stability checks. | Is the build ready to test further? |
| 2. Identify the change | Read the change note or ticket and list the functions it touches and their nearest neighbours. | What must be checked, and what can wait? |
| 3. Run a few focused checks | Exercise the fixed behaviour and the closely related paths, narrow but with real depth. | Does the change do what the requirement says? |
| 4. Pass or reject | If the checks pass, move on to wider testing. If not, reject the build and report the defect. | Spend more test effort, or stop now? |
| 5. Record the result | Note which checks ran, which defects were found and what was left untested, with reasons. | What does the release note say? |
How is sanity testing different from smoke and regression testing?
| Sanity testing | Smoke testing | Regression testing | |
|---|---|---|---|
| Question it answers | Does this change work as intended? | Is the build stable enough to test? | Did the change break anything that worked before? |
| Scope | Narrow and deep on a few areas | Broad and shallow across core functions | Wide, across all areas the change could affect |
| Typical timing | After a fix or small change, on a stable build | Straight after a new build | After the change is accepted, before release |
| Typical style | Often manual or exploratory | Often automated | Preferred for automation |
| Outcome | Reject the build or widen testing | Accept or reject the build for testing | Confidence that existing behaviour holds |
The ISTQB glossary, as reproduced on istqb-glossary.page defines regression testing as testing of a previously tested program following modification, to show that a change has not introduced or exposed defects in unchanged areas. Sanity testing is the cheap check that decides whether paying for that is worthwhile. For the smoke side, see smoke vs regression testing.
When should you run a sanity test, and when is it not enough?
| Situation | Run a sanity test? | Why |
|---|---|---|
| Hot fix for a single defect, little time | Yes | It confirms the fix works before you spend a full regression cycle. |
| Minor change to existing functionality | Yes | It checks the change and its nearest neighbours quickly. |
| New build that may be unstable | Not first | Run a smoke test first. Sanity checks assume the build already starts and its core works. |
| Major release with new modules | Not enough | Needs full functional, integration and regression testing. See system testing. |
| Performance, load or security risk | Not enough | Quick manual checks cannot show these. Use dedicated automated testing. |
What does a sanity test look like in practice?
This is an illustrative example, not a case study. Suppose a defect report says a discount code is ignored at checkout, and the developer ships a fix.
| Check | What the tester does | Why it belongs in the sanity set |
|---|---|---|
| The fix itself | Apply the discount code to a basket and confirm the total changes | This is the change under test |
| Nearest neighbours | Add and remove items, change quantity, then re-check the total | The pricing code is shared with these paths |
| Direct dependants | Complete the order and check the order summary shows the same total | A wrong total here would block the release |
| Left for later | Payment methods, delivery options, account pages | Outside the change; leave for regression, and note it as untested |
Which techniques and tools support sanity testing?
Most sanity checks start as a short manual checklist. Automation helps when the same checks repeat on every build. Two documented patterns are below, and they work with whichever test tool you already use.
| Approach | How it helps | Source |
|---|---|---|
| Manual checklist | The tester lists the change, its neighbours and what is out of scope, then records the result. | Common testing practice |
| Tagged automated tests | Playwright lets you tag tests with an @-prefixed tag and run only those with the --grep option, so a small sanity subset runs on every build. | Playwright documentation (read 13 Nov 2026) |
| Pipeline gate | In Azure Pipelines, stages run in order by default, and a stage runs only if the stages it depends on succeeded unless you set a custom condition. A sanity stage can therefore sit between build and the wider test stages. | Microsoft Learn (read 13 Nov 2026) |
To see where this sits in a wider testing strategy, read shift-left testing, continuous testing in DevOps and TestOps best practices.
What are the best practices for sanity testing?
Keep it short. Limit the set to the changed behaviour and its closest neighbours. If it grows into a full cycle, it has become regression testing.
Prioritise the critical path. Check what the business cannot release without, such as a failed checkout or login.
Reject quickly. If a sanity check fails, return the build at once instead of continuing with deeper testing.
Automate the stable checks. Move repeated checks into tagged tests or a pipeline stage, and keep the exploratory checks manual.
Record what ran. Note the executed cases, the defects with their status and anything left untested, with reasons, in the release note.
Review the set often. Update the checks as the product changes so they stay relevant.
How do sanity checks fit when AI agents change the code?
As coding and testing agents propose more small changes, the number of builds that need a fast gate grows. The sanity check is a natural place to put an explicit rule: the agent may merge only when the focused checks pass, and a person decides when they do not. Agentic software testing covers the agents, tools and controls that make this safe.
According to its site, AgentQA tests agent outputs and workflows continuously, and ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows. Both are worth a look if sanity gates for agent-made changes are on your roadmap.
Related testing guides
- Smoke testing vs sanity testing
- Smoke testing vs regression testing
- What is regression testing?
- System testing tools and best practices
- Functional vs non-functional testing
- Agentic software testing
To map one release decision your testing agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions
What is sanity testing in simple terms?
It is a quick check, usually after a bug fix or small change, that the changed behaviour works as intended. If it fails, the build goes back to the developer. It is usually treated as a subset of regression testing.
Is sanity testing the same as smoke testing?
Not in common team practice. Smoke testing asks whether a build is stable enough to test, and sanity testing asks whether a specific change works. The ISTQB glossary, as reproduced on istqb-glossary.page, does list sanity test as a synonym of smoke test, so define the terms in your own test plan.
Is sanity testing manual or automated?
Either. It is often manual or exploratory because the checks depend on the change, but stable repeated checks can be tagged and run automatically, for example with Playwright tags and the --grep option.
When should you not rely on sanity testing?
Do not rely on it for major releases, new modules, or performance, load and security risk. It is narrow by design and does not replace regression or system testing.
What should be recorded after a sanity test?
Record the cases executed, the defects found with a status, and anything left untested with the reason, so the release note shows what was and was not checked.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE