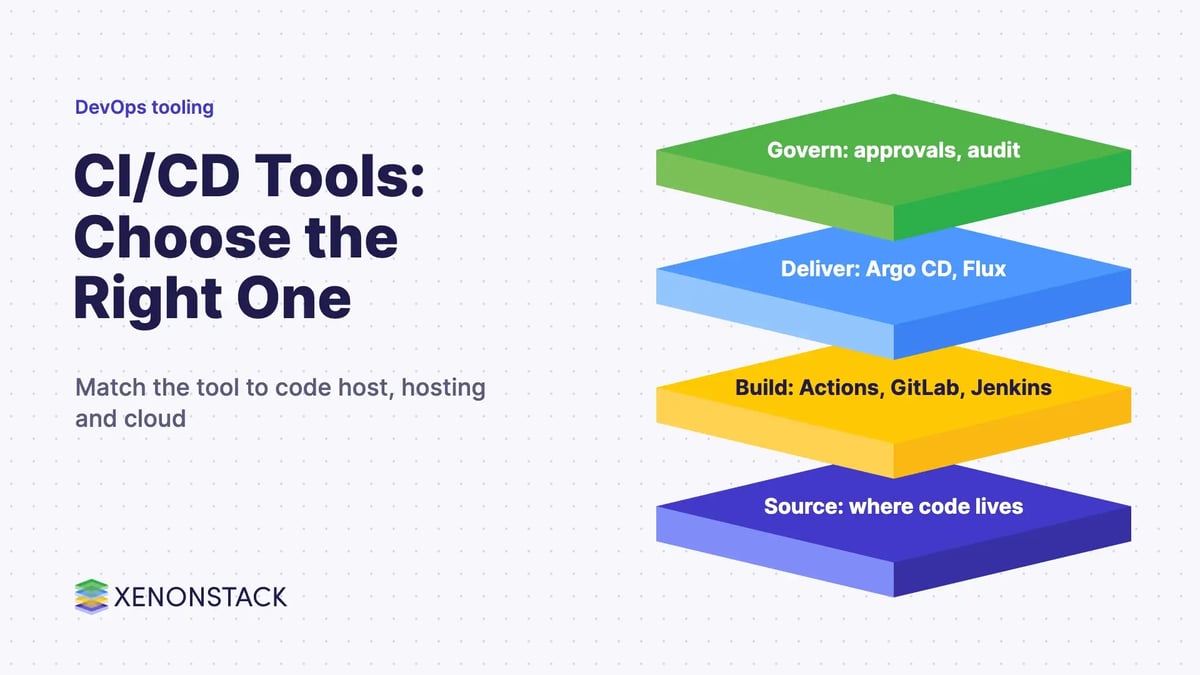
Key takeaway
- Open source DevOps tools for 2026 by pipeline stage: CI/CD, testing, IaC, GitOps and monitoring, plus licence changes such as Terraform BSL and OpenTofu.
The best open source DevOps tools in 2026 are the ones that cover each pipeline stage with a project that is still maintained and licensed the way you expect: Git hosting with GitLab, CI with Jenkins or GitLab CI, testing with JUnit, Selenium, Playwright, k6 and ZAP, infrastructure as code with OpenTofu or Ansible, GitOps with Argo CD or Flux, and observability with Prometheus, OpenTelemetry and Grafana. Several familiar names have changed licence or status since 2023, so a tool list from a few years ago is no longer a safe buying guide. If security is your first concern, read our guide to the DevSecOps pipeline, tools and governance; if you run mainly on AWS, compare this list with our AWS DevOps tools guide.
This guide is written for CTOs, platform leads and solution architects who own the toolchain decision. It groups tools by stage, shows which ones changed licence (Terraform, Packer, Grafana, Elasticsearch, Zabbix, Puppet), and gives an adoption order and a short list of cases where adding another tool is the wrong move.
What are DevOps tools and how should you group them?
DevOps tools automate the hand-offs between writing code, testing it, releasing it and running it. DevOps is a process and lifecycle first and a toolchain second, so the useful way to choose tools is by stage: one primary tool per stage, with clear inputs and outputs between them.
| Pipeline stage | Open source options | What the stage does |
|---|---|---|
| Source control | Git with GitLab (self-managed) | Versioned code, branching, merge requests and code review |
| Continuous integration | Jenkins, GitLab CI | Builds and tests every change so integration problems surface early |
| Build | Apache Maven, Gradle, GNU Make | Compiles code and packages artefacts from a single build definition |
| Testing | JUnit 6, Mocha, Selenium, Playwright, Grafana k6, ZAP | Unit, browser, load and dynamic security tests inside the pipeline |
| Infrastructure and configuration | OpenTofu, Ansible, Chef, OpenVox | Declares infrastructure and enforces server state from code |
| Orchestration and GitOps | Kubernetes, Docker Swarm mode, Argo CD, Flux | Schedules containers and keeps clusters in sync with Git |
| Monitoring and observability | Prometheus, OpenTelemetry, Jaeger, Grafana, Zabbix, OpenSearch | Metrics, traces, logs and dashboards for running services |
| Collaboration | Rocket.Chat (self-hosted), wiki tools | ChatOps alerts, incident rooms and runbooks |
The short XenonStack video below gives an overview of DevOps tools.
Video: List of best DevOps tools, from XenonStack.
Which open source DevOps tools changed licence or status?
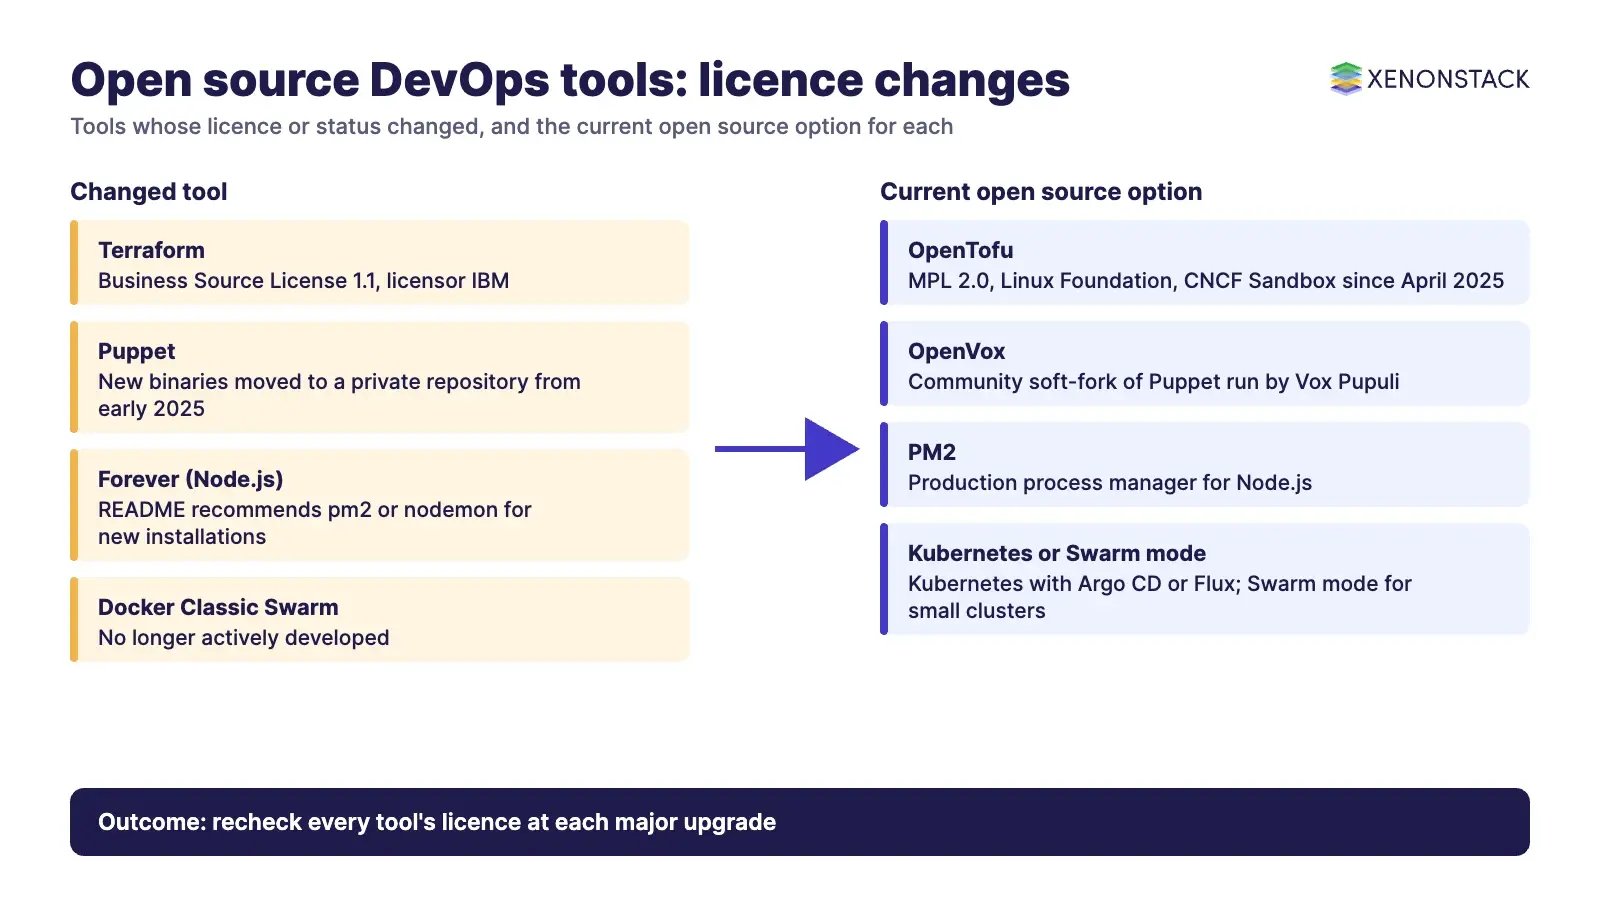
Licence changes matter because they decide whether you can embed a tool in a product, offer it as a service, or keep using community builds. These are the changes we confirmed on each project's own site or repository in November 2026.
| Tool | Current licence or status | What it means for you |
|---|---|---|
| Terraform | Business Source License 1.1, licensor IBM; each version converts to MPL 2.0 four years after publication | Not an open source licence. Production use is limited by the Additional Use Grant, so check it if you build a competing service. |
| OpenTofu | MPL 2.0, Linux Foundation project; CNCF Sandbox since 23 April 2025; version 1.13.0 released | Drop-in replacement for Terraform for teams that need an open source IaC licence. |
| Packer | Business Source License 1.1 from version 1.10.0, licensor IBM | Same review as Terraform before you rely on it for golden images. |
| Grafana, Loki, Tempo | Relicensed from Apache 2.0 to AGPLv3 (announced 20 April 2021); k6 is also AGPLv3 | Free to use; modifying and exposing them over a network brings source-sharing obligations. |
| Elasticsearch and Kibana | AGPL added as a licence option next to ELv2 and SSPL (announced 29 August 2024) | Elasticsearch and Kibana can be used under an open source licence again; OpenSearch remains the Apache 2.0 alternative. |
| OpenSearch | Apache 2.0, hosted by the OpenSearch Software Foundation, a Linux Foundation project | Permissive licence for search and log analytics. |
| Zabbix | AGPLv3 from version 7.0; up to 6.4 was GPLv2 | Recheck your obligations when you upgrade from 6.x. |
| Puppet | Source stays Apache 2.0, but new binaries and packages moved to a private repository from early 2025; above 25 nodes needs a commercial licence for the hardened builds | Community users either build from source or move to OpenVox. |
| OpenVox | Community soft-fork of Puppet run by Vox Pupuli | Keeps an open source package path for Puppet code. |
| Forever (Node.js) | README recommends pm2 or nodemon for new installations | Do not start new work on Forever. |
| Docker Swarm | Swarm mode is built into current Docker Engine; Classic Swarm is no longer actively developed | Use Swarm mode only for small clusters; Kubernetes is the default for most enterprises. |
Which source control and CI/CD tools fit an enterprise pipeline?
For source control and CI most enterprises choose between a self-managed GitLab instance and Jenkins attached to their existing Git host. Both are mature; the decision is about how much you want in one product versus how much flexibility you want in plugins. For a wider comparison of CI/CD products, see our DevOps automation tools guide. For teams starting to let AI agents act on pipelines, ElixirClaw is an agentic OS platform to build, orchestrate and govern AI agents and automation workflows while keeping humans in control.
| Tool | Licence and status | When it fits |
|---|---|---|
| Jenkins | MIT licence; describes itself as the leading open source automation server | You need a highly extensible CI server that works with any Git host and many build tools. |
| GitLab | Core code under the MIT Expat licence; code in the ee/ directory is under GitLab's separate EE licence. CE and EE share one codebase since 2019 | You want source control, merge requests, issues and CI in one self-managed product. |
| Argo CD | Part of the Argo project, a CNCF graduated project since 6 December 2022 | You deploy to Kubernetes and want Git to be the source of truth for releases. |
| Flux | CNCF graduated since 30 November 2022 | You prefer a lighter GitOps toolkit built from Kubernetes controllers. |
Build tools sit inside CI. Apache Maven manages a Java project's build, reporting and documentation from its Project Object Model; Gradle focuses on build automation across languages; GNU Make remains common for C, C++ and container image builds.
Which DevOps testing tools belong in the pipeline?
DevOps testing tools give you a real-time measure of risk in every release. Put fast tests early and slow tests later, so a failed unit test stops the pipeline in minutes and browser, load and security tests run on candidates that already passed.
| Test type | Tool | Current state | Pipeline stage |
|---|---|---|---|
| Unit (JVM) | JUnit | JUnit 6 is the current generation | Every commit |
| Unit (JavaScript) | Mocha | JavaScript test framework for Node.js | Every commit |
| Browser end to end | Selenium | Built on the W3C WebDriver standard; Selenium 4.52 released 29 October 2026; Grid runs sessions in parallel | Merge or nightly |
| Browser end to end | Playwright | One API for Chromium, Firefox and WebKit; TypeScript, Python, .NET and Java | Merge or nightly |
| Load and performance | Grafana k6 | AGPLv3 licence | Release candidate |
| Dynamic security (DAST) | ZAP | Free and open source web app scanner, now branded ZAP by Checkmarx | Release candidate and scheduled scans |
Choose Playwright when your team writes tests in TypeScript or Python and wants one API across three browser engines. Choose Selenium when you need the widest language and browser vendor support or already run a Selenium Grid.
Which infrastructure as code and configuration tools should you choose?
Infrastructure as code turns servers, networks and cloud accounts into reviewed, versioned files. The licence change above is the main new factor: teams that need an open source licence now pick OpenTofu, while teams already on Terraform with a HashiCorp or IBM relationship can stay.
| Tool | Model | When it fits | Status |
|---|---|---|---|
| OpenTofu | Declarative IaC, Terraform-compatible | New open source IaC estates or Terraform users who need MPL 2.0 | Linux Foundation, CNCF Sandbox |
| Terraform | Declarative IaC | Existing estates and teams using HashiCorp commercial products | BSL 1.1 |
| Ansible | Agentless automation from a control node and inventory | Configuration, patching and app deployment across mixed servers | Open source; documented at docs.ansible.com |
| Chef | Agent-based configuration management | Existing Chef estates | Review current packaging and licence terms before new adoption |
| Puppet or OpenVox | Agent-based, declarative state | Large existing Puppet estates | Puppet builds now private; OpenVox open source fork |
Ansible automates the management of remote systems and controls their desired state from a control node, an inventory of managed hosts and modules. That makes it a good partner to OpenTofu: OpenTofu creates the infrastructure, Ansible configures what runs on it.
Which container orchestration and GitOps tools are current?
Kubernetes is the default orchestrator for enterprise containers and a CNCF graduated project since 6 March 2018. The project maintains release branches for the three most recent minor versions; in November 2026 those are 1.37, 1.36 and 1.35, with 1.37.1 released on 15 September 2026. Plan upgrades at least once a year so clusters stay on a supported version. Our guide to Docker container architecture and monitoring covers the container layer underneath.
Docker Swarm mode is still built into Docker Engine and suits small clusters with simple needs. For anything larger, run Kubernetes with Argo CD or Flux so every deployment is a Git commit that can be reviewed, audited and rolled back.
Which monitoring and observability tools should you use?
Observability has consolidated around open standards. Prometheus is an open source monitoring system with a dimensional data model, and all its components are under Apache 2.0. OpenTelemetry provides vendor-neutral instrumentation for traces, metrics and logs, and Jaeger stores and shows distributed traces.
| Tool | Role | Licence or CNCF status |
|---|---|---|
| Prometheus | Metrics collection and alerting | Apache 2.0; CNCF graduated 9 August 2018 |
| OpenTelemetry | Instrumentation standard for traces, metrics and logs | CNCF graduated 11 May 2026 |
| Jaeger | Distributed tracing | CNCF graduated 31 October 2019 |
| Grafana, Loki, Tempo | Dashboards, logs and traces | AGPLv3 |
| Zabbix | Infrastructure and network monitoring | AGPLv3 from 7.0 |
| OpenSearch or Elastic Stack | Log search and analytics | Apache 2.0 (OpenSearch); AGPL, ELv2 or SSPL (Elastic) |
When alert volume grows faster than the on-call team, the next step is automated triage. AgentSRE applies agentic AI to incident management, with agents that automate detection, root cause analysis and remediation.
How do governance, security and cost shape the toolchain?
- Licence review. Keep a register of every tool's licence and recheck it at each major upgrade. Terraform, Packer, Zabbix 7.0 and Puppet packaging all changed under users who did not change anything themselves.
- Supply chain security. Pin tool versions, scan dependencies and run DAST before release. The controls, frameworks and gates are covered in our DevSecOps guide.
- Access control. Use single sign-on and role-based access for Git, CI and cluster tools, and keep secrets in a dedicated secrets manager rather than CI variables.
- Cost. Open source removes licence fees, not running costs. Budget for hosting, upgrades, plugin maintenance and the engineers who own each tool.
- Agent actions. As AI agents start to open merge requests and run deployments, AgentGRC keeps autonomous agent actions inside policy, with the audit trail risk teams need.
In what order should an enterprise adopt DevOps tools?
- Standardise on one Git platform and a branching model.
- Add CI that builds and runs unit tests on every change.
- Add an artefact repository and versioned builds so every release can be traced to a commit.
- Move infrastructure into OpenTofu or Terraform and configuration into Ansible.
- Add browser, load and DAST testing at the release-candidate stage.
- Adopt Kubernetes with Argo CD or Flux for GitOps deployments.
- Instrument services with OpenTelemetry, collect metrics in Prometheus and build Grafana dashboards tied to service level objectives.
- Review licences, access and cost every quarter and retire tools nobody owns.
When should you not add another DevOps tool?
- When an existing tool already covers the stage. Two CI servers or two GitOps controllers double the upgrade and security work.
- When nobody will own it. An unpatched Jenkins plugin or stale Grafana instance is a security risk, not a capability.
- When the licence does not fit your business model, for example a BSL or AGPL tool inside a product you sell as a service, until legal has reviewed it.
- When the team is small and a managed service is cheaper than running the open source version yourself.
How can XenonStack help with your DevOps toolchain?
XenonStack designs and runs DevOps pipelines for enterprises, from CI/CD and infrastructure as code to Kubernetes and observability. See our DevOps consulting services for how we assess an existing toolchain and plan the move to supported, correctly licensed tools.
To map one release or rollback decision your pipeline and agents should make, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
Frequently asked questions about DevOps tools
What are the main categories of open source DevOps tools?
Most toolchains cover source control, continuous integration, build, testing, artefact storage, infrastructure as code and configuration, container orchestration and GitOps, monitoring and observability, and collaboration. Pick one primary tool per stage and connect them through the pipeline.
Is Terraform still open source?
No. Terraform is released under the Business Source License 1.1, with IBM named as licensor. Each version converts to MPL 2.0 four years after publication. OpenTofu is the MPL 2.0 fork under the Linux Foundation and was accepted to the CNCF Sandbox on 23 April 2025.
Which DevOps testing tools should a pipeline include?
A practical set is JUnit 6 or Mocha for unit tests, Selenium or Playwright for browser tests, Grafana k6 for load tests and ZAP for dynamic security scans. Run fast unit tests on every commit and slower browser, load and security tests at later pipeline stages.
Which monitoring tools are CNCF graduated projects?
Prometheus graduated on 9 August 2018, Jaeger on 31 October 2019 and OpenTelemetry on 11 May 2026. Kubernetes, Argo and Flux are also graduated CNCF projects.
What changed for Puppet open source users?
Perforce said in November 2024 that new Puppet binaries and packages would move to a private repository from early 2025, while the source stays under Apache 2.0. Vox Pupuli now maintains OpenVox, a community soft-fork that aims to stay compatible with Puppet.
Do AGPL tools such as Grafana and k6 affect enterprise use?
Using them internally is usually straightforward. The AGPL asks you to offer source code to network users if you modify the software and let them interact with it over a network, so legal teams should review any modified version you expose as a service.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE