Key takeaway
- Security testing in DevOps explained: which tests to run (SCA, SAST, DAST, penetration), tools, OWASP and NIST standards, and how to build a programme.
Security testing in DevOps is the set of tests that check whether an application, its dependencies and its infrastructure can be attacked, run as part of delivery and not as a separate review before launch. The useful question for a leader is not which scanner to buy but which tests you run, who acts on the findings, and what evidence a release carries.
This guide is about the tests themselves: what each type finds, which tools exist, and how to build a testing programme with owners. For where checks sit in a pipeline read DevSecOps in CI/CD; for task lists see the DevSecOps checklist; for the wider practice see continuous security, SecDevOps and DevSecOps. For a definition of each test type read types of security testing.
What is security testing in DevOps, and why does it matter?
Security testing looks for weaknesses that let an attacker read, change or disrupt data and services. In DevOps the tests run repeatedly, so a flaw is reported while the change is small. The NIST Technical Guide to Information Security Testing and Assessment (SP 800-115) describes testing as a way to find vulnerabilities in systems or networks and to verify compliance with policies. NIST lists the publication as final, dated September 2008, with no later revision shown on its page, so use it for method and read current tool documentation for specifics.
Three properties guide what you test: confidentiality (only authorised people see data), integrity (data is not altered without authority) and availability (services stay reachable for authorised users). Each test below maps to at least one of them.
Which types of security test should a DevOps team run?
The OWASP DevSecOps Guideline lists the activities a pipeline can include: secret detection in repositories, software composition analysis (SCA), static analysis (SAST), infrastructure-as-code scanning, supply chain controls, interactive testing (IAST), API security, dynamic testing (DAST) and compliance checks. It treats the list as a starting point to extend over time. The table below adds the manual tests that sit beside them.
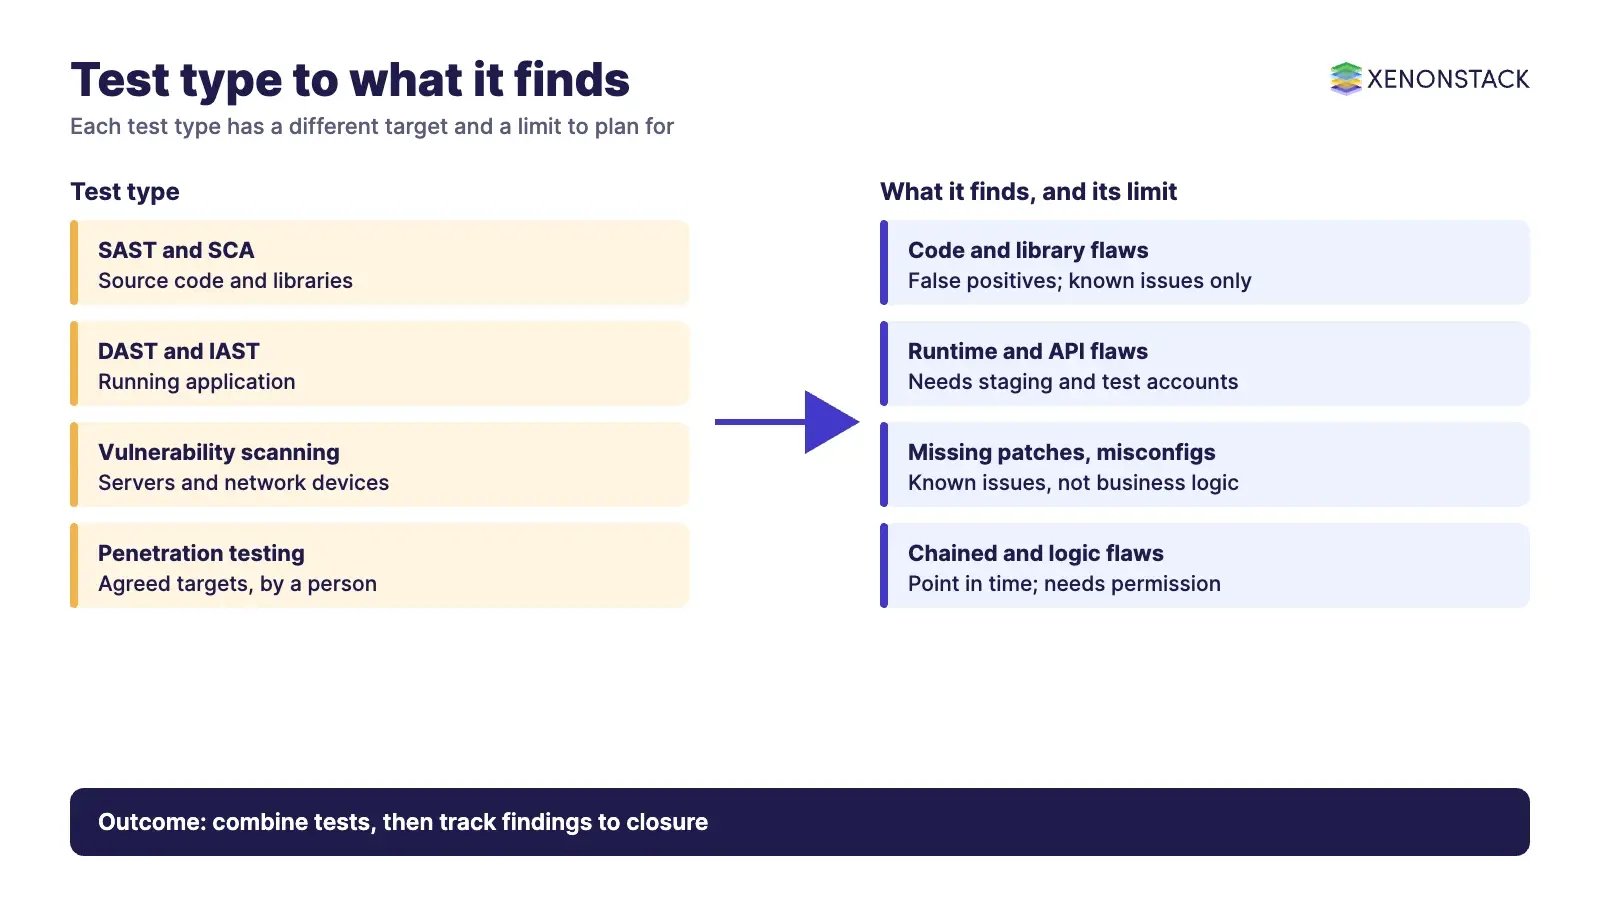
| Test | What it does | Best for | Limit to plan for |
|---|---|---|---|
| Vulnerability scanning | Compares systems and services with known weaknesses, missing patches and misconfigurations | Servers, containers, network devices | Finds known issues, not business-logic flaws |
| SAST | Reads source code without running it | Early feedback to developers | False positives; language support varies |
| SCA | Checks third-party libraries against known vulnerabilities | Open source dependencies | Only known, published issues |
| DAST | Attacks a running application from outside | Web apps and APIs in a test environment | Needs a stable environment and test accounts |
| IAST | Observes the application from inside while tests run | Teams with strong functional test coverage | Only code paths the tests exercise |
| Penetration testing | A person simulates an attacker against agreed targets | Releases and changes with high business risk | Point in time; slower; needs scoping and permission |
| Security review and risk assessment | Examines design, configuration and risk rating | Design decisions and architecture changes | Depends on reviewer skill |
Penetration testing and ethical hacking are related but not identical; see ethical hacking vs penetration testing and our list of penetration testing tools. Test only systems you own or have written permission to test.
What should you test for, and which standards define it?
Three OWASP resources give a shared vocabulary. The OWASP Top 10 names the current edition as 2025. The Application Security Verification Standard (ASVS) is a framework of security requirements for designing, developing and testing web applications and services; its page lists version 5.0.0, published 30 May 2025, and says it can serve as a metric, as guidance and as a basis for procurement. The Web Security Testing Guide (WSTG) is the testing framework for web applications and services; its page lists v4.2 as the latest release, with v5.0 in development.
| Source | Use it to | Status read on 13 Nov 2026 |
|---|---|---|
| OWASP ASVS | Decide what a secure application must do, and what testers check | 5.0.0 listed as stable |
| OWASP WSTG | Structure manual and automated web tests | v4.2 latest release; v5.0 in development |
| OWASP Top 10 | Prioritise common risk categories for awareness and triage | 2025 edition named as current |
| NIST SP 800-115 | Plan and run technical security tests and assessments | Final, September 2008 |
Injection and scripting flaws, such as SQL injection and cross-site scripting (XSS), and request forgery (CSRF) remain standard test targets. SQL injection happens when untrusted input changes the meaning of a database query. XSS lets script run in another user's browser. CSRF makes a logged-in user's browser send an unwanted request. Prevention guidance for the browser side, such as content security policy, is in our post on HTTP security headers.
Which security testing tools are worth knowing?
Tool choice depends on what you test and what your team will triage. The three below are examples with public documentation, not a ranking. Commercial scanners from other vendors also exist; check each vendor's page for current product names and editions before buying.
| Tool | What it is, per its own page | Fits | Check before use |
|---|---|---|---|
| ZAP | Free, open source web app scanner; credited as ZAP by Checkmarx; its FAQ covers its Automation Framework | DAST in test environments | Confirm licence and automation options in its docs |
| Nikto | Web server scanner; code under GNU GPL v3; scan categories include misconfigurations, default files, information disclosure, injection and authentication bypass | Quick web server checks | Database files carry separate terms; GitHub Releases section shows no release |
| Nessus | Vulnerability assessment scanner; per its page finds flaws, missing patches and misconfigurations across operating systems, devices and applications; Professional and Expert editions listed | Infrastructure vulnerability scanning | Licensing and web scan limits on the vendor page |
Run scanners only against systems you are authorised to test, and start in a staging environment. An unauthenticated scan of a login-protected application finds little, so give DAST tools test accounts.
What are the common challenges, and how do you handle them?
| Challenge | Why it happens | What helps |
|---|---|---|
| Cultural resistance | Teams see security as a gate that slows delivery | Report findings to the developer who made the change, with a fix path, and agree severity rules together |
| Skill gaps | Few engineers know security testing techniques | Train developers on the Top 10; keep penetration testing with specialists |
| Tool overload | Many scanners, overlapping findings | Choose a small set per test type; send results to one backlog |
| Integration complexity | Scanners and CI tools do not fit cleanly | Pilot on one service; run new scans in report-only mode first |
| Resource limits | Budget and people are finite | Test by risk: more depth for internet-facing and sensitive systems |
How do you build a security testing programme?
This sequence is XenonStack guidance, not a standard. Adjust it to your risk and team size.
| Step | Action | Result |
|---|---|---|
| 1 | List applications and rate them by data sensitivity and exposure | Testing effort follows risk |
| 2 | Pick a requirement baseline such as OWASP ASVS | Testers and developers share one definition of secure |
| 3 | Automate SCA, SAST and secret detection on every change | Fast feedback on code and dependencies |
| 4 | Run DAST and API tests against staging with test accounts | Runtime flaws found before release |
| 5 | Schedule penetration tests for high-risk releases | Human-found issues that tools miss |
| 6 | Track findings to closure with an owner and a due date | Evidence that issues are fixed, not only found |
What are the trade-offs, and when is a test the wrong choice?
A blocking test that the team cannot triage is worse than none, because people learn to ignore it. Do not run intrusive scans on production without agreement and a rollback plan. Do not treat a clean scan as proof of safety: scanners find known patterns, and business-logic flaws, weak design and stolen credentials need review, testing by people and monitoring. Keep proof of each test run, since auditors and customers ask for evidence.
Where AI coding agents or other automation make changes, their output needs the same tests as human code. ElixirData says its Context OS keeps governed context, versioned policy and decision traces in one decision layer above AI agents, and AgentGRC says it keeps autonomous agent actions inside policy, with the audit trail risk teams need (according to its site).
To map one release decision your agents should make, such as whether a build with open findings may ship, and the context and policy it depends on, book a Context Workshop. See what happens in the workshop.
FAQs on security testing in DevOps
What is security testing in DevOps?
It is the practice of running security tests, such as SCA, SAST, DAST, vulnerability scans and penetration tests, as part of the delivery process so that weaknesses are found while changes are small. NIST SP 800-115 describes security testing as a way to find vulnerabilities and verify compliance with policy.
What is the difference between SAST, DAST and IAST?
SAST reads source code without running it. DAST attacks a running application from outside. IAST observes the application from inside while tests run. The OWASP DevSecOps Guideline lists all three among pipeline activities, and teams usually combine them because they find different problems.
Which standards guide security testing?
The OWASP Application Security Verification Standard (version 5.0.0 on its page), the OWASP Web Security Testing Guide (v4.2 latest release, v5.0 in development), the OWASP Top 10 (2025 edition) and NIST SP 800-115. Confirm current versions on each official page.
Is penetration testing part of DevOps security testing?
Yes, but it is a human-led, point-in-time test rather than an automated one. Most teams automate scanning on every change and schedule penetration tests for high-risk releases, always with written permission and agreed scope.
Can a security scan prove an application is safe?
No. Scanners find known patterns and misconfigurations. They do not reliably find business-logic flaws or design weaknesses, so combine automated tests with review, manual testing and monitoring.
Ready to put AI agents to work? See an ElixirClaw demo: the agentic OS to build, orchestrate and govern AI agents across your enterprise systems.
Explore the XenonStack platform family: ElixirData · ElixirClaw · ElixirHub · NexaStack · MetaSecure · Neural AI · AgentGRC · AgentSRE · AgentAnalyst · AgentInstruct · AgentRAI · AgentScrum · AgentSearch · AgentForce · AI Aviator · SAIF Aviator · CohortIQ · XenonStack AI · XenonStack UAE